Every Line of Code Might Be a Recall Risk
Navigating the SDV Engineering Stack

27 Oct, 2026. 6 minutes read
Introduction: The SDV Paradox
Software-Defined Vehicles (SDVs) promise a fundamental shift in how cars are designed, improved, and experienced. Rather than having their capabilities largely fixed at production, SDVs use software to control and evolve vehicle functions such as infotainment, energy management, driver assistance, and chassis behavior. Moreover, they leverage Over-The-Air (OTA) updates in order to introduce new capabilities, resolve defects, and improve performance long after a vehicle leaves the factory.
The commercial momentum behind SDVs has moved faster than a shared, practical definition of what it takes to build one safely. For Original Equipment Manufacturers (OEMs), software is increasingly becoming a survival strategy, as it provides a route to differentiation, recurring digital services, and faster innovation cycles. However, more software introduces more dependencies, more interfaces, and more potential failure modes. For instance, any defect in a single software component can affect an entire fleet, which can prompt a recall in the worst case. Therefore, the SDV transition is an essential engineering transformation that goes far beyond a product-roadmap change. SDV success is about moving quickly while continuously demonstrating safety, cybersecurity, and regulatory compliance. This is largely a matter of establishing a well-structured and integrated engineering process.
Redefining the SDV: Beyond "More Software"
An SDV vehicle platform is designed around the expectation of continuous change, which means that adding a layer of code over an existing vehicle architecture is not enough. Over the years, traditional automotive electronics have evolved through adding distributed electronic control units (ECUs). ECUs are dedicated to specific functions and often supplied through separate vendor ecosystems. The ECU model works well for stable, well-bounded functions. However, it becomes increasingly difficult to manage when a vehicle must support OTA updates, centralized computing, service-oriented software, and features that span multiple vehicle domains.
This leads to the need for a profound architectural shift. OEMs are moving toward consolidated compute, zonal architectures, common software platforms, and reusable middleware. They are also trying to own a larger share of the software stack. This is because they would like to reduce supplier costs, while at the same time lowering their dependency on dozens of disconnected software and hardware environments, gaining access to operational data, and shortening the time from insight to deployed features.
The SDV transition is happening worldwide, yet not in a uniform way. North American manufacturers face acute commercial pressure around cost, speed, software monetization, and recall exposure. European OEMs are balancing software transformation with mature regulatory requirements, premium-brand expectations, and predictive-maintenance opportunities. In China, rapid EV adoption, domestic digital ecosystems, connected services, and automated-driving development are accelerating the SDV model. Japan’s evolution is often shaped by especially stringent validation and safety expectations, which favor disciplined, incremental platform transformations. Broadly speaking, North America, Europe, and Asia-Pacific are all major SDV growth regions, yet their market drivers and adoption patterns differ substantially. These growth trends point to a common denominator: software is becoming the primary mechanism through which automotive value is created, maintained, and differentiated.
The Engineering Bottleneck: Complexity vs. Capability
Nowadays, the central SDV challenge is the need to deal with complexity without clear interfaces, useful abstractions, traceable dependencies, and analyzable behavior. A modern vehicle programme may involve hundreds of suppliers, multiple chip architectures, different operating environments, proprietary tools, open-source libraries, middleware platforms, cloud services, code generators, and increasingly AI-assisted development workflows. Each of these components is fully defensible in isolation. Nevertheless, considerable risks emerge at the interfaces. This is where assumptions conflict, versions drift, updates cross domain boundaries, and evidence that was valid for one configuration is no longer sufficient for another.
This fragmentation makes the development lifecycle extremely challenging. For example, requirements may be stored in one system while implementation and test results sit in several others. At the same time, a compiler, debugger, static-analysis platform, test environment, and traceability system may each produce valuable evidence, yet not necessarily in a coherent chain. In this landscape, engineers can struggle to understand whether a small code change affects timing, memory allocation, safety mechanisms, cybersecurity controls, diagnostic behavior, or downstream vehicle functions. Furthermore, it is common for certification and release teams to face a manually assembled evidence burden.
The reality is also clearly reflected on the modern recall problem. Vehicle recalls are no longer only associated with a defective mechanical part or a faulty ECU. Increasingly, risk can originate in third-party software, vulnerable or poorly governed open-source dependencies, code-generation artefacts, configuration mistakes, compiler behaviors, or AI-generated code that has not been properly verified. The software supply chain has therefore become part of the vehicle itself and consequently, its safety, security, and compliance case must extend across the entire development lifecycle
In conventional vehicle architectures, functional safety and cybersecurity were often managed as interdependent, yet distinct disciplines. In SDVs, that separation no longer holds. OTA delivery pipelines, cloud connectivity, centralized compute platforms, vehicle APIs, remote diagnostics, service-oriented architectures, and software-defined functions all expand the attack surface. At the same time, the impact of an error or compromise can become broader because software is more deeply integrated across vehicle domains.
In this context, any cyber vulnerability can create a safety consequence. Teams must therefore establish evidence not only that a feature behaves correctly under intended conditions, but that it remains resilient under malicious, unexpected, degraded, and misused conditions.
 Source: TASKING
AI-Assisted Development Still Requires Engineering Discipline
In recent years, AI-assisted engineering has significantly helped developers to navigate large codebases, draft implementation options, generate test scaffolding, summarize documentation, identify patterns, and automate repetitive tasks. All this provides a foundation for expanding engineering capacity at a time when automotive software complexity is increasing faster than many organizations can hire or train specialists. However, AI does not change the obligation to verify the result. Any AI-generated function must be treated as an engineering artefact subject to the same discipline as human-authored work. That means controlled requirements, peer review, traceability, reproducible builds, static and dynamic analysis, target-level testing, coverage assessment where appropriate, configuration management, and safety-case evidence.
The standards landscape reflects, supports and reinforces the above-listed principles:
ISO 26262 establishes the core functional-safety lifecycle for road-vehicle electrical and electronic systems.
ISO 21448, known as Safety of the Intended Functionality (SOTIF), addresses unreasonable risk caused by functional insufficiencies or reasonably foreseeable misuse, even when no conventional hardware or software fault is present. This distinction is critical for Advanced Driver Assistance Systems (ADAS). A perception system, for example, may be functioning according to its implemented code but still produce unsafe outcomes because of insufficient training coverage, uncertain sensing conditions, edge cases, or foreseeable human misuse.
ISO/PAS 8800 extends the discussion to safety-related aspects of AI-based electrical and electronic systems in road vehicles, with relevance for machine-learning elements and their integration into ISO 26262-oriented processes.
The message is clear: AI can increase engineering capacity, but it cannot replace engineering discipline. Responsible AI adoption therefore requires standards-based controls, traceability, verification, and evidence to be embedded in the engineering workflow.
The TASKING Perspective: A Unified Approach to Embedded Development
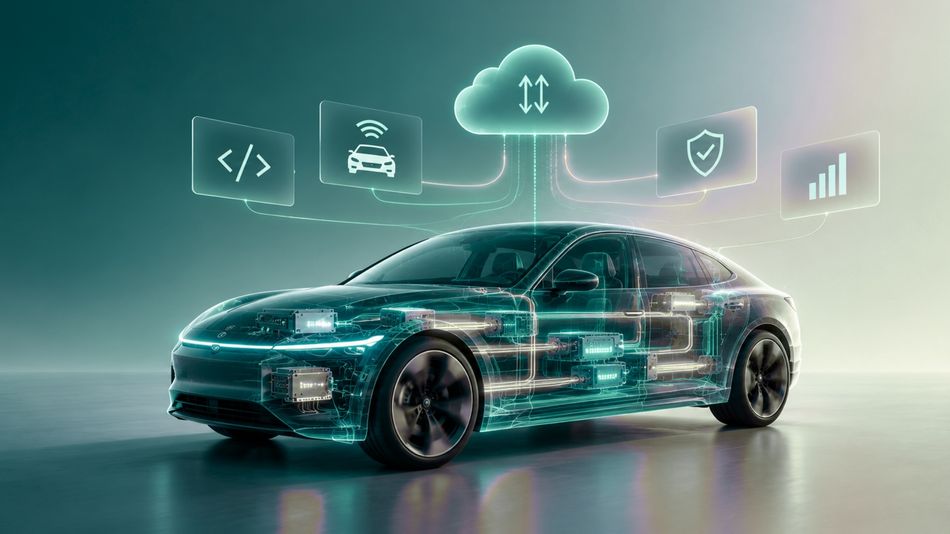
The company’s unified toolchain brings together Compilers, BlueBox debuggers, the winIDEA development environment, and LDRA capabilities for static analysis and unit verification across the development lifecycle. The value lies not in any individual tool, but in connecting their capabilities and the evidence they produce. Compilation, debugging, testing, static analysis, and verification each provide a different perspective on the software and its behavior on the target. Combined with traceability and analysis of data, control, and timing coupling, these capabilities provide a more coherent basis for demonstrating software quality, safety, and compliance. Such evidence becomes significantly harder to establish and maintain when the toolchain is fragmented.
The SDV engineering response to the above-listed challenges cannot be a growing collection of disconnected point tools. Industry expectations are shifting from optimizing individual stages (e.g., compile, debug, test, analysis, requirements, certification) to holistically optimizing the complete lifecycle end-to-end. This is the logic behind TASKING’s approach.
This shifts the focus from optimizing individual development stages to improving the efficiency and consistency of the complete engineering lifecycle. As a prominent example, the company’s recent RH850 offering brings integrated compile, debug, and test & verification capabilities for the Renesas RH850 architecture. This environment is also TÜV certified for functional safety and cybersecurity.
TASKING’s approach also reflects the importance of a tight silicon-and-toolchain ecosystem. Automotive software must execute predictably on specific microcontrollers and multicore hardware. TASKING supports major automotive architectures (e.g., Infineon AURIX/TriCore, NXP S32K, RISC-V, and Renesas RH850). Its tools are included in various Infineon DRIVECORE software bundles. Such alignment reduces integration overhead and gives engineering teams more consistent workflows across hardware targets.
TASKING's goal is to help engineering teams manage growing software complexity more efficiently. By streamlining development, analysis, test, and verification, the company enables teams to bring embedded software to market without compromising the automotive industry's demanding safety and cybersecurity standards.
Conclusion: The Roadmap to SDV Success
The SDV era requires a marriage of speed and trust. Vehicle manufacturers must deliver software improvements quickly. However, they must do so with a continuous ability to explain what changed, what it affects, how it was tested, and why it remains safe and secure.
Software-defined vehicles are already a reality. The actual challenge is to engineer increasingly complex software efficiently and at scale. As architectures consolidate, OTA releases become routine, and software volumes keep rising, the pressure to deliver reliable, verifiable software continues to grow. In this landscape, competitive advantage will come from the ability to generate continuous, auditable evidence of safety, cybersecurity, quality, and compliance at the pace of innovation.
To learn more in person, visit the TASKING Conference on 29 October 2026 in Munich, Germany.